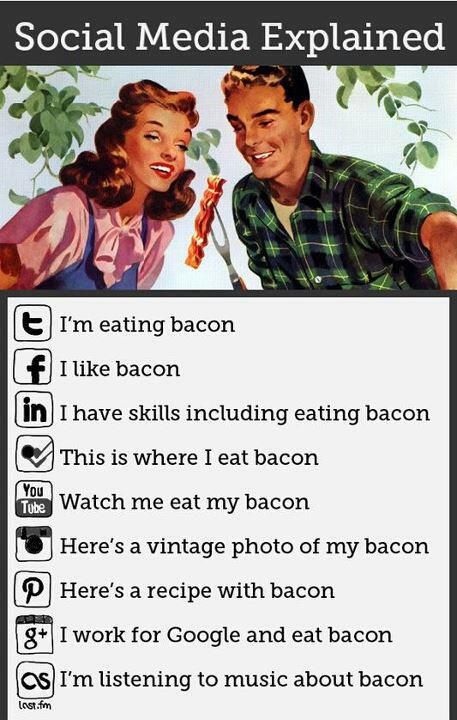
Still not getting social media? Here’s a delightfully non-kosher, non-halal explanation. From Pinterest, of course.
5
MAR
MAR
0
Share
Still not getting social media? Here’s a delightfully non-kosher, non-halal explanation. From Pinterest, of course.
 2017 is promising to be another difficult year for cyber-defenders who are protecting company and government networks from attack. Here are what I think will be the top attack vectors this year.
Business Email Compromise
CEOs and other C suite officers will increasingly be targeted for email account hijacking. This is an easy exploit to run because high ranking employees and officers often ...
Continue Reading → US-CERT just released more information about the Grizzly Steppe cybercrime group who has been fingered for hacking the DNC and US voter registration databases. The short report, titled Enhanced Analysis of GRIZZLY STEPPE Activity, makes interesting reading, especially if you are interested in finding out more about state-sponsored political espionage. See pages 4-7 for the main story.
The Grizzly Steppe group is ...
Continue Reading →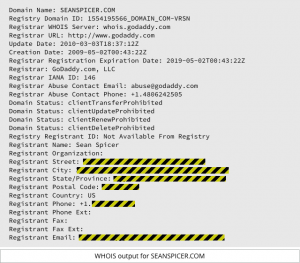 I will start out by admitting that I hate Domain Privacy. But I just read a story in Naked Security on February 9th that is causing me to reevaluate my opinion. It turns out that the new White House press secretary, Sean Spicer, has a personal website at www.seanspicer.com. The website has been turned into a private site, but the WHOIS ...
 Remember late last year when the Russian Cyber Army was supposedly hacking the Vermont electrical grid?
Well, squirrels and other critters are still doing more damage to the electric grid than cyber-attacks have. When are we going to round up all these little terrorists and ship them off to Gitmo?
I got my OFFICIAL DAISY RED RYDER RANGE MODEL 1938 AIR RIFLE BB GUN ...
Continue Reading → I read an interesting article on Naked Security the other day about how Hamas had used Facebook and social engineering tactics to trick Israeli soldiers into installing surveillance malware. The malware allowed Hamas to track the soldiers using the phone’s GPS, and to turn on the microphone and video to actually listen in and and watch their targets. Hamas undoubtedly picked up the ...
 As a regular reader of this blog, you are probably using a long, unique, 20 character password with two-factor authentication, and a password manager to keep it all straight. But let’s say that you fall for a phishing scam, and give away the password to your email account. The attacker can now use your email account to request password reset emails from your other online accounts, and you have yourself one ...
Facebook has added USB key security to it’s two-factor authentication options. Previously, Facebook users could add the additional security of two-factor authentication to their account by using the Facebook app to receive a six digit one-time passcode, or by having the code sent to their smart phone via SMS text message. Facebook now supports the open-source Universal 2 Factor (U2F) standard established by the FIDO Alliance, such as the Yubikey from ...