On May 13, in Austin, Texas, the 40th Annual O.Henry Pun-Off Championship was held. Since I love puns, and am frequently guilty of punning in public, I thought this was an interesting tid-bit to pass along. Enjoy! (or not)
I am often asked to explain the difference between a security compliance audit, a vulnerability assessment, and a penetration test. These exercises do many of the same things, but to a different degree. A security compliance audit is like a 5K fun run, where a vulnerabilty assessment is more like a marathon. A penetration test is an iron man competition.
In the course ...
Continue Reading →JUN
US-CERT sent an announcement on May 9th about new resources for small and medium size business owners and managers. Protecting Small Businesses can be found on the FTC website. It includes information about:
- Protecting your business from scams
- Cybersecurity
- Data breach response
- Protecting personal information
There are also helpful videos about:
- Building security into software development
- Controlling access to data
- Defending against ...
JUN
Back on February 22nd, we discussed Facebook’s new Delegated Account Recovery feature. Basically, if you should for some reason forget your password to any account, or lose your two-factor authentication device (smartphone), and can no longer get into your account, Facebook will help you recover the account, as long as it is one that is enrolled with Facebook.
This is not the same thing as password managers like DashLane or LastPass, ...
Continue Reading →JUN
From Pinterest
-
Continue Reading →
4Share
JUN
On Wednesday we took a look at a collection of mostly web-based reconnaissance tools. Today we are taking it to the next level and actually attempting to find and exploit vulnerabilties.
Kali Linux – This is a pen-testers version of Linux that comes fully loaded with over a hundred testing applications. Kali can be installed in any old laptop you have laying around, installed as a virtual ...
Continue Reading →JUN
When starting an security assessment or penetration test with a new client, often the first step is information gathering or reconnaissance. Sure, you could just ask the client for the information you want, but where’s the fun in that? Here is a list of tools to use to find information that they may not know is publicly available.
Google hacking or Google “dorks” – Johnny Long literally wrote the book about ...
Continue Reading →MAY
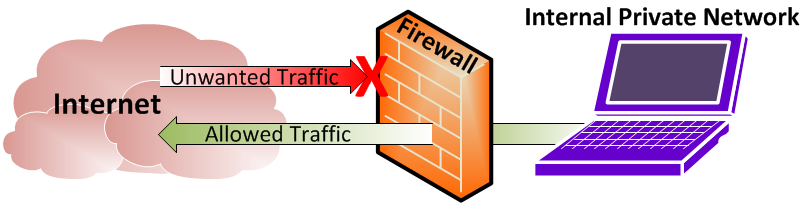
I had an interesting question from a client last month. They were looking for guidance on “egress filtering.” Egress filtering is the concept of tuning your perimeter defenses (firewalls, routers, IDS*, and UTM* devices) to review and restrict the flow of information that is leaving your network.
Historically, most perimeter defenses are are designed to keep ...
Continue Reading →MAY
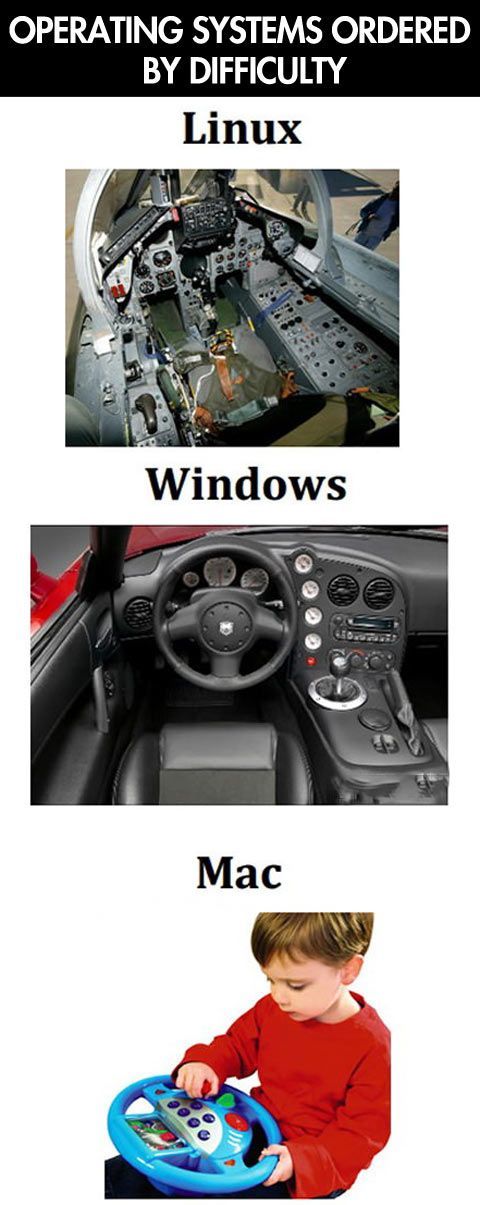
I have used all three.
My analysis: Linux = fun, Windows = practical, Apple = toy. Sorry Apple fans.
Continue Reading →MAY
It is my belief that if you are planning a crime, you might as well go for the glory. The jail time is the same whether you steal $50,000 or $50 million.
I’m not sure if this is the biggest phishing scam ever, but it is the biggest I’ve heard of. A Lithuanian man named Evaldas Rimasaukas devised a scheme that extracted over $100 million from Google and Facebook. He achieved this ...
Continue Reading →MAY