Your Tax Dollars At Work – Governmental Surveillance

We know that the US government is spying on us.  Just how deep the surveillance goes is a question that is hard to answer.  If you are one of those people who thinks this surveillance is OK because you “have nothing to hide,”  I suppose you could skip this article.  But here’s my question – why do you get upset when your identity is stolen by a cyber-criminal, but yet you are unmoved when your own government does the same ...

Continue Reading →
0

9-11 Remembered

Today is the 18th anniversary of a day that I will never forget.  I was driving home from dropping my son off at school, and listening to the radio when they started reporting that a plane had flown into the World Trade Center.  I made it home in time to see the second plane crash into the second tower on television.  Still gives ...

Continue Reading →
0

Internet Anonymity – A Case Study

Who is Will McLauglin?  The Campaign for Privacy?  or Dennis Anon and Privacy.net?

I’ve been writing this blog long enough that I receive regular submissions for guest content, infographics and other sort of suggestions for article topics. As long as the submissions are legitimate and on topic, I am generally happy to post them.  My next post is one of those times.  My efforts at verifying the source has been an ...

Continue Reading →
0

Sunday Funnies – Quantum Computing Explained

First – It’s my birthday, so Happy Birthday to me!  It is ok to send me gifts.  ;-Q

The rule with USB drives, as we all know, is it will not plug in until the third try.  Joe Soucheray of Garage Logic fame has a similar rule known as the “50/50/90 Rule.”  Basically, any time you have a 50/50 chance, you are 90% likely to choose the wrong answer.  The USB Third Try Rule extends on that concept.  ...

Continue Reading →
0

Weekend Update

A quick Saturday digest of cybersecurity news articles from other sources.


[INFOGRAPHIC] Introducing The Psychology of Passwords

From LastPass – It feels like almost every day there’s another data breach in the news, or a case of user credentials up for sale on the Dark Web. Despite the headlines, and repeated warnings from experts about weak passwords and the dangers of password reuse, users have yet to change their ...

Continue Reading →
0

Data Breach – What To Do Next

Your IT manager comes to you with a look on his or her face that is a combination of panic, shock, and depression.  “We’ve been breached, and it looks like they got into the customer database, but I’m not sure how long they’ve been on our network, and what else they might have done.”  Do you know what you need to do next?

In previous articles we have covered Continue Reading →

1

SIM Swap Fraud Is Growing

In the middle of the day your cell phone mysteriously goes dead.  Later on, when you call the cell phone carrier, you find out that someone else pretending to be you has visited a store and claimed to have lost your phone.  Customer service agents moved your mobile number to a new SIM card on a new phone, and using your phone and other personal information gathered earlier through phishing ...

Continue Reading →
0

How Valuable Is Cybersecurity Training?

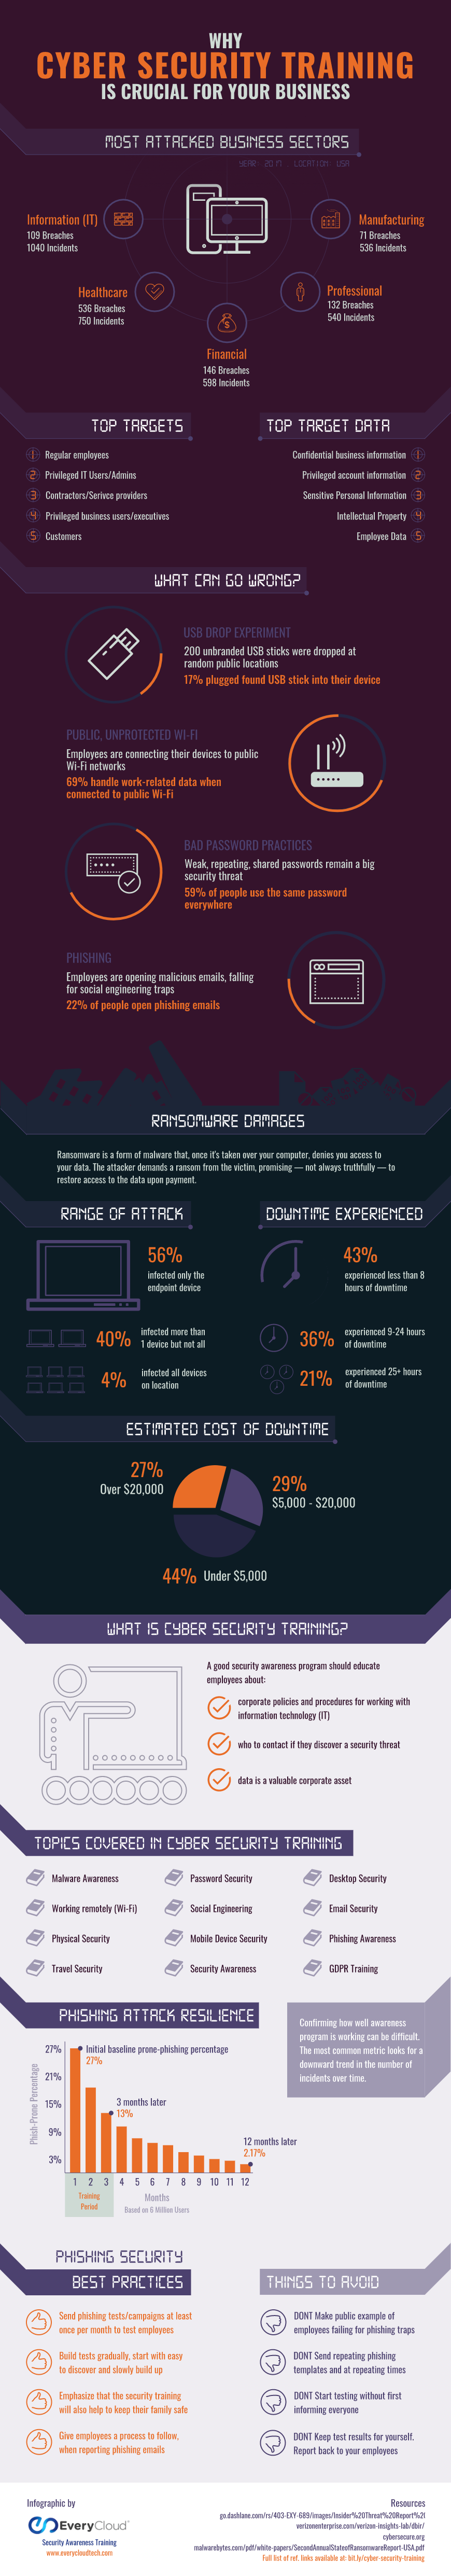
We are a big proponent of cybersecurity awareness training for your employees. Humans are always the weakest link in the cybersecurity chain, so enlisting your employees in the fight against cyber-attacks has to begin with some basic training, and ideally continue with periodic refreshers, and activities like phishing simulation exercises.

Today’s infographic is a guest post by security training firm Everycloud Technologies.

Continue Reading →
0
Page 142 of 279 «...110120130140141142143144...»