From Facebook. On my Pinterest feed.
What kind of disease can you catch from an old typewriter? The Smith-Corona Virus, of course.

 A quick Saturday digest of cybersecurity news articles from other sources.
Ransomware attack forces 2-day shutdown of natural gas pipeline
The US Department of Homeland Security (DHS) on Tuesday said that an infection by an unidentified ransomware strain forced the shutdown of a natural-gas pipeline for two days.
Crypto AG Fallout: Cyber Rivals Call the U.S. ...
Continue Reading →FEB
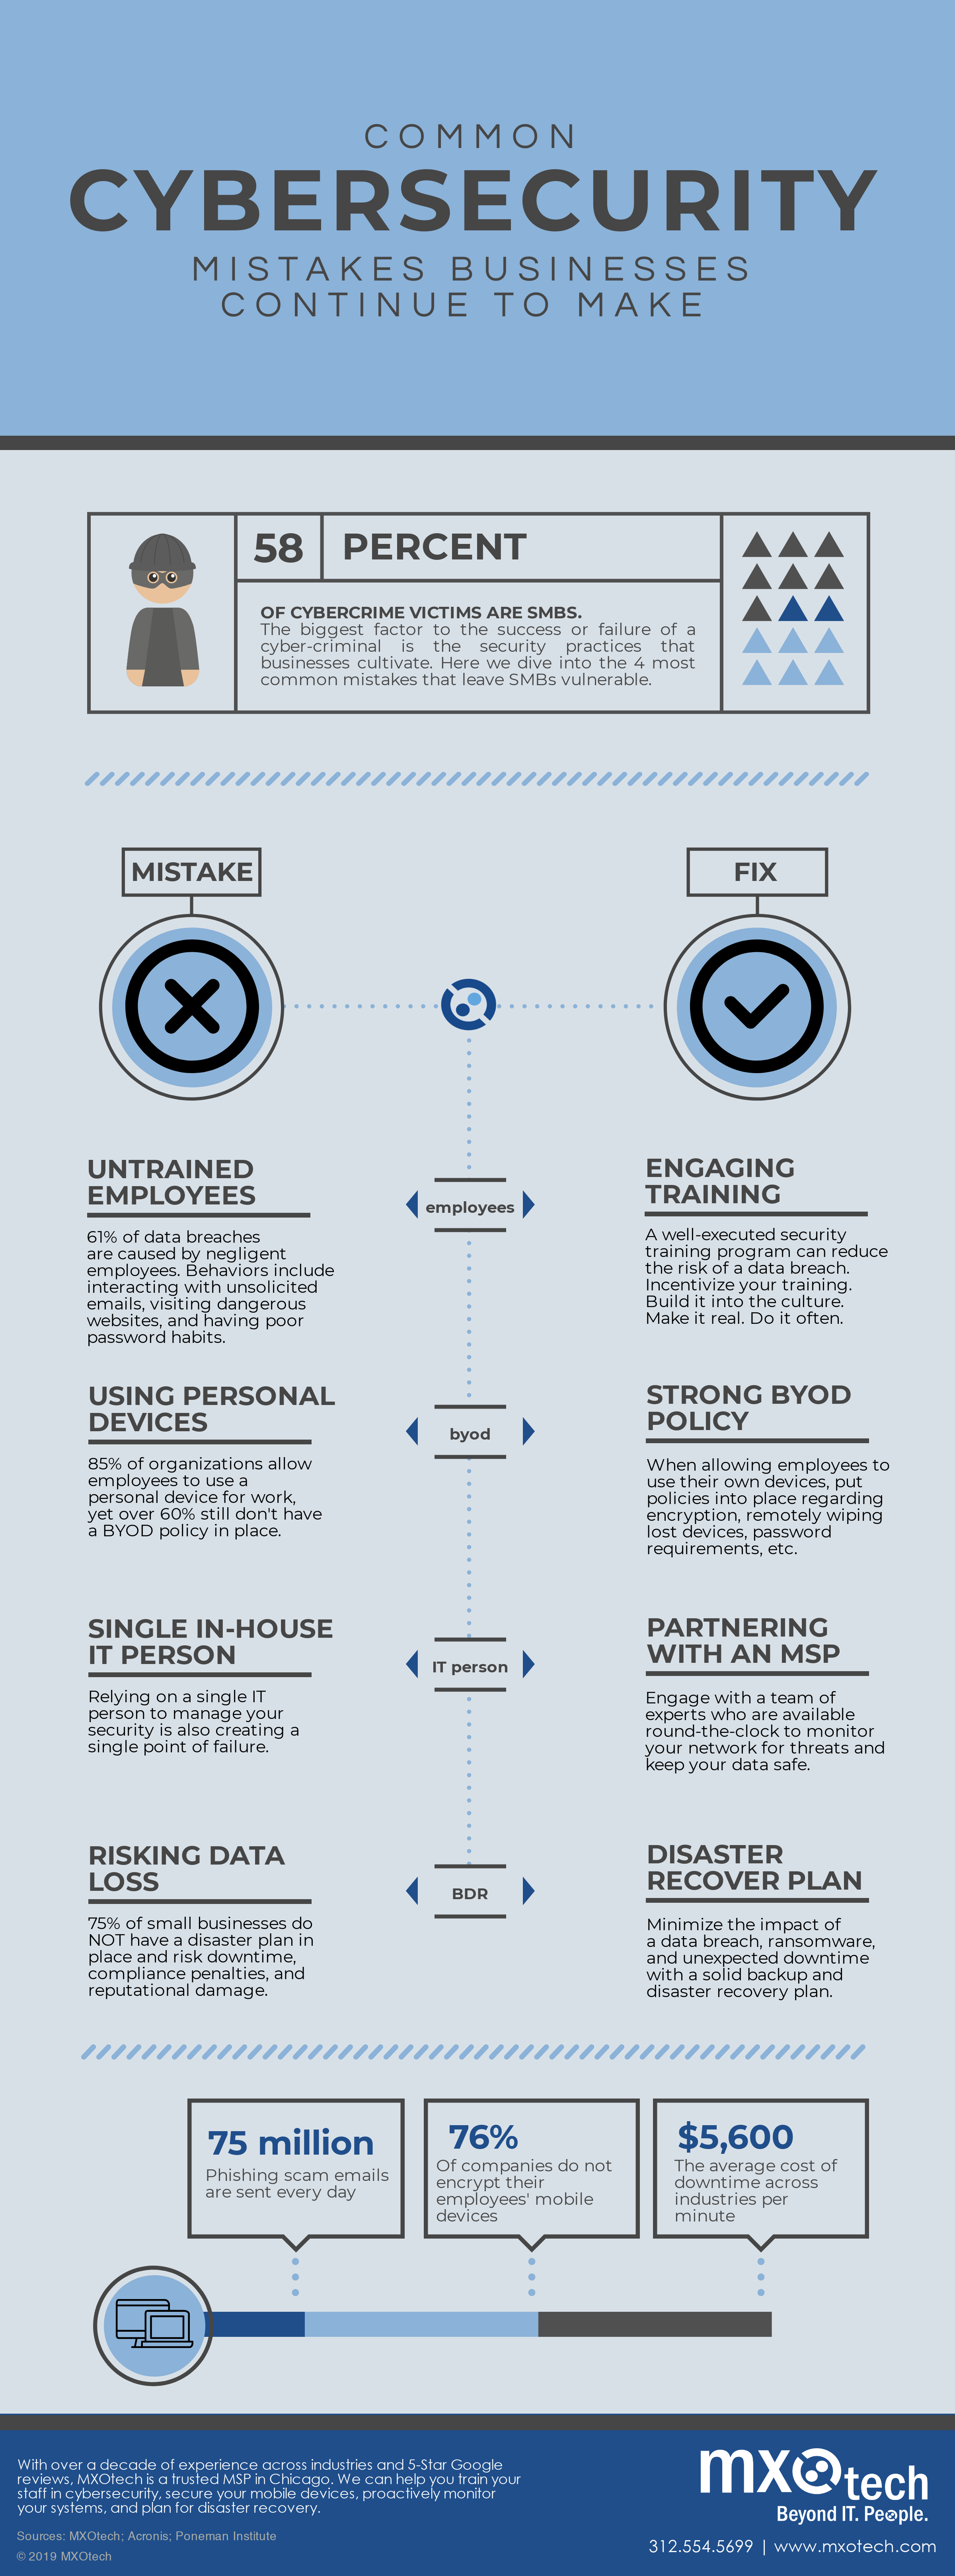
A guest infographic from Chicago area managed service provider MXOTech. I recommend clicking thorough the link so you can read the complete article.
 The Corp.com domain is for sale, and depending on who ends up owning it, this could be catastrophic for companies that use Windows domains and Active Directory. It basically is Microsoft’s fault (of course), except it is not. The problem is that many admins who were setting up Active Directory domains for their company followed the directions a little too exactly. In ...
FEB
 Insider threats, the risks and dangers caused by malicious or careless acts performed by your own employees, contractors, and trusted vendors is perhaps the most difficult cyber attack to detect and defend. What happens when a member of your own IT department turns to the dark side?
Between 2015 and 2019, IT executive Hicham Kabbaj scammed his employer out of $6 million dollars for servers, other products, and installation services by ...
Continue Reading →FEB
From Pinterest. This may be one of the reasons I am getting happier as I get older – CRS syndrome – Can’t Remember Shit.
A quick Saturday digest of cybersecurity news articles from other sources.
Hidden Cobra: North Korean Malicious Cyber Activity
Original release date: February 14, 2020
The Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI), and the Department of Defense (DoD) have identified the following malware variants used by the North Korean government. The U.S. Government refers to malicious cyber activity by the North Korean government ...
Continue Reading →FEB
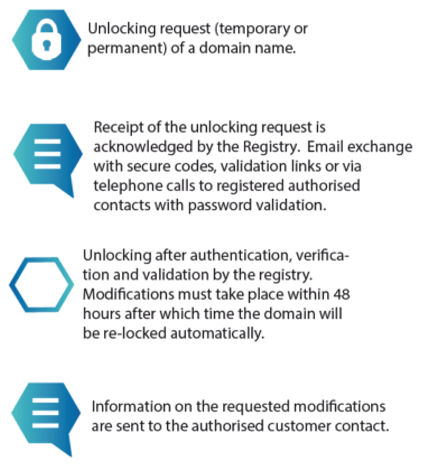 How can you have a domain lock or client transfer prohibited, and still lose your domain name to attackers? Domain lock was invented to prevent unauthorized parties from stealing your domain name. As reported by Brian Krebs on January 24, 2020, that happened to a well regarded service that helps Web sites detect and block fraud. They had a domain lock but ...
FEB
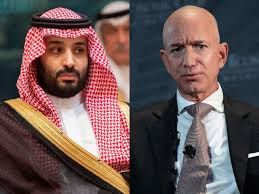 Or The Strange Case of Jeff Bezos’ IPhone and the Saudi Crown Prince
The evidence says that the Saudi Arabian Crown Prince, Mohammed bin Salman (aka MBS) engineered a way to hack Jeff Bezos’ cell phone. Just why MBS would be interested in Jeff, Jeff’s phone, or Jeff’s life is an interesting question, with surprising answers.
It seems that MBS invited Jeff Bezos to a private party, and during the course of ...
Continue Reading →FEB
 Today I am running a guest post by Panda Security, courtesy of my friends at Siege Media. As you may have heard, 2019 was the year of ransomware. The target? The public sector. With variations such as Cryptolocker, German Wiper and Robinhood, there was a shocking number of government ransomware attacks this past year. ...
FEB